Regex Injection
 By Malcolm McDonald Founder, Editor-in-ChiefAuthor of Grokking Web Application Security
Regular expressions are frequently used in web-development, but can be abused by attackers.
- Prevalence
- Common
- Exploitability
- Easy
- Impact
- Worrying
What is regex injection?
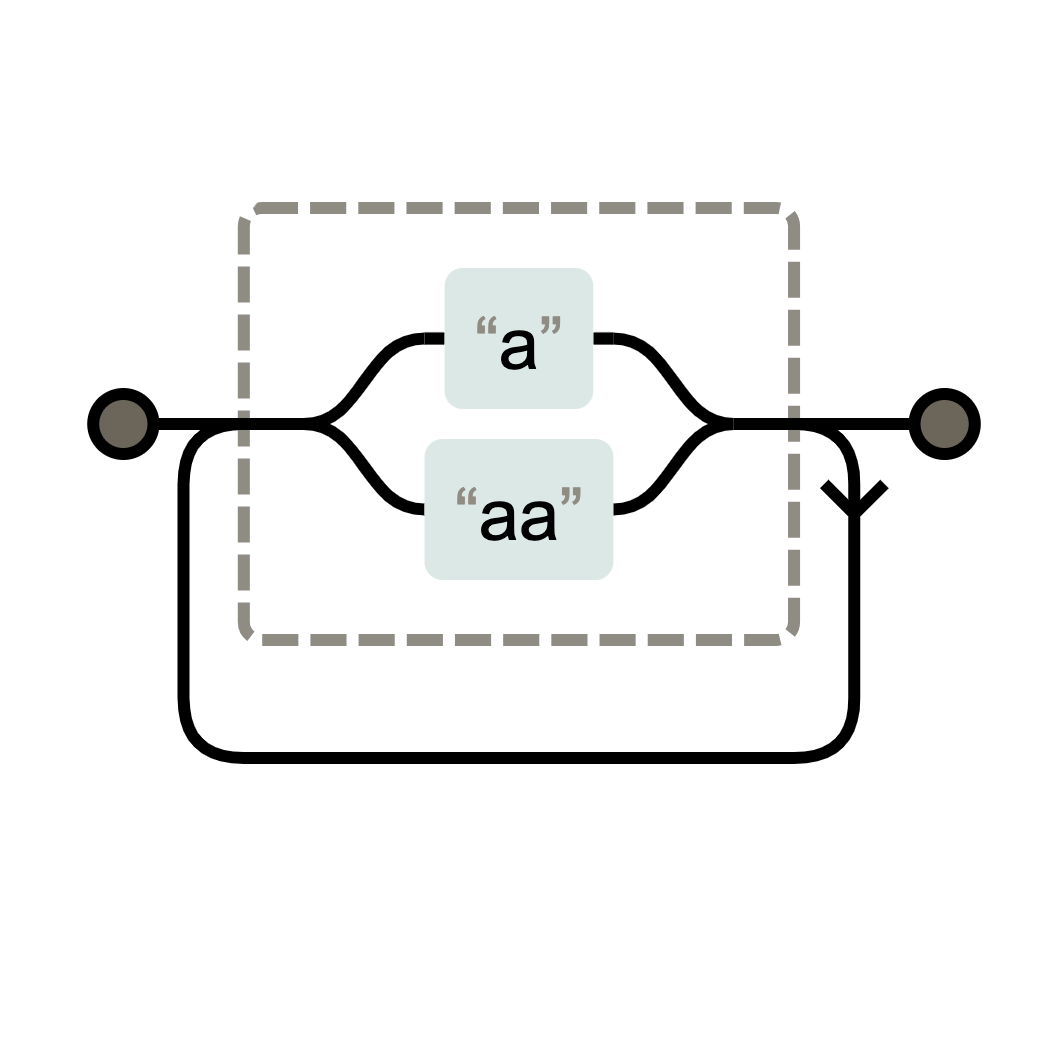
Regex injection is an injection attack in which an attacker supplies input that is used to build a regular expression, or that exploits a poorly designed one already in your code. The resulting expression takes an enormous amount of computing power to evaluate, tying up the server. This denial of service is known as ReDoS.
What you'll learn
- How regular expression engines backtrack on ambiguous patterns
- How crafted input triggers catastrophic backtracking and ties up a server
- Why you should never build regular expressions from untrusted input
Where this lesson counts
OWASP Top 10
Untrusted input reaches an interpreter as part of a command or query, including SQL, OS and cross-site scripting.
Learn more about A05PCI DSS 4.0
Requirement 6.2.4: engineering techniques must prevent injection, data-structure, cryptographic, business-logic and access-control attacks in bespoke software.
Learn more about 6.2.4This lesson includes
-
Regex Injection lab
See how regular expressions are evaluated and why an ambiguous pattern forces the engine to backtrack. The lab explains how attackers type crafted strings into search boxes and other inputs to trigger catastrophic backtracking, tying up the server until real users can't get through.
-
How to prevent Regex Injection
The prevention guide covers four approaches:
- Don't Generate Regular Expressions from Untrusted Input
- Use a Search Index for Complex Searches
- Avoid Catastrophic Backtracking
- Automatically Detect Unsafe Regular Expressions
-
Regex Injection quiz
Three questions. Passing marks the lesson complete.
Sources
- CWE-185 MITRE
Related lessons
Browse all 45 lessons
Denial of Service Attacks
Sometimes attackers don't need to hack your website, they just want to make it unavailable to others.
SQL Injection
If you are vulnerable to SQL Injection, attackers can run arbitrary commands against your database.
Command Execution
If your application calls out to the OS, you need to be sure command strings are securely constructed.