SQL Injection
 By Malcolm McDonald Founder, Editor-in-ChiefAuthor of Grokking Web Application Security
If you are vulnerable to SQL Injection, attackers can run arbitrary commands against your database.
- Prevalence
- Occasional
- Exploitability
- Easy
- Impact
- Devastating
What is SQL injection?
SQL injection is an injection attack in which an attacker submits crafted input that an application pastes into a database query, changing what the query does. It happens when SQL statements are built by concatenating strings with untrusted input. Attackers use it to bypass logins, read or alter data, and delete entire tables.
What you'll learn
- How string concatenation lets attacker input rewrite a SQL query
- How to spot an injection vulnerability from an error message and the code
- Why parameterized statements are the most reliable defense
Where this lesson counts
OWASP Top 10
Untrusted input reaches an interpreter as part of a command or query, including SQL, OS and cross-site scripting.
Learn more about A05PCI DSS v4.0.1
Requirement 6.2.4: engineering techniques must prevent injection, data-structure, cryptographic, business-logic and access-control attacks in bespoke software.
Injection flaws are the first attack class named in requirement 6.2.4.
Learn more about 6.2.4Requirement 6.4.1: public-facing web applications must be protected against known attacks by regular vulnerability review or an automated technical solution.
Learn more about 6.4.1This lesson includes
SQL Injection lab
Attack a login form backed by a real database running in your browser. Start with a single quote that crashes the app, read the SQL error in the logs, see the vulnerable code, then use ' or 1=1-- as the password to log in.
How to prevent SQL Injection
The prevention guide covers four approaches, including:
- Parameterized Statements
- Object Relational Mapping
- Escaping Inputs
SQL Injection quiz
Three questions. Passing marks the lesson complete.
Sources
- SQL injection PortSwigger
- Exploiting SQL Injection Acunetix
- SQL Injection Cheatsheet Netsparker
- Bobby Tables xkcd
Related lessons
Browse all 45 lessons
Command Execution
If your application calls out to the OS, you need to be sure command strings are securely constructed.
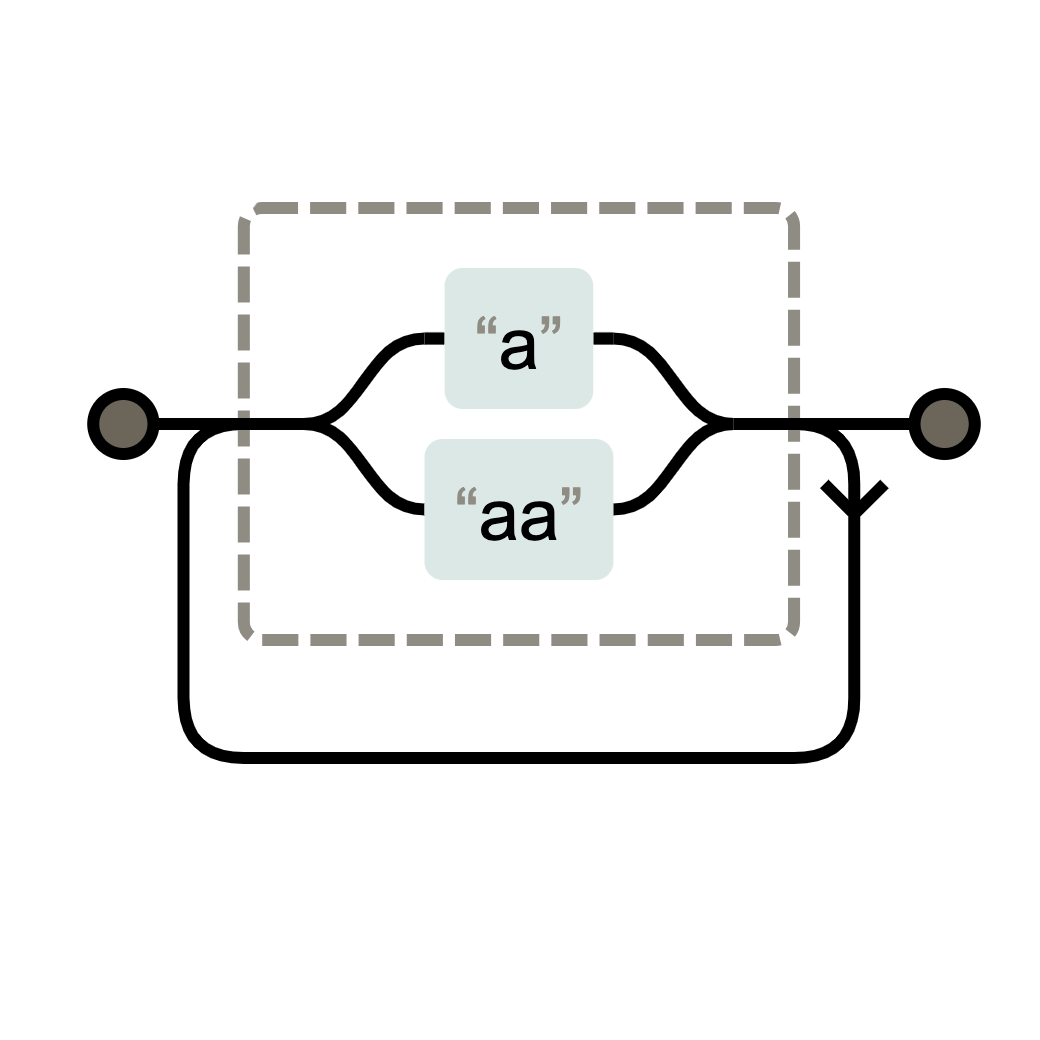
Regex Injection
Regular expressions are frequently used in web-development, but can be abused by attackers.
Cross-Site Scripting
If your site allows users to add content, you need to be sure that attackers cannot inject malicious JavaScript.
Information Leakage
Revealing system information helps an attacker learn about your tech stack.